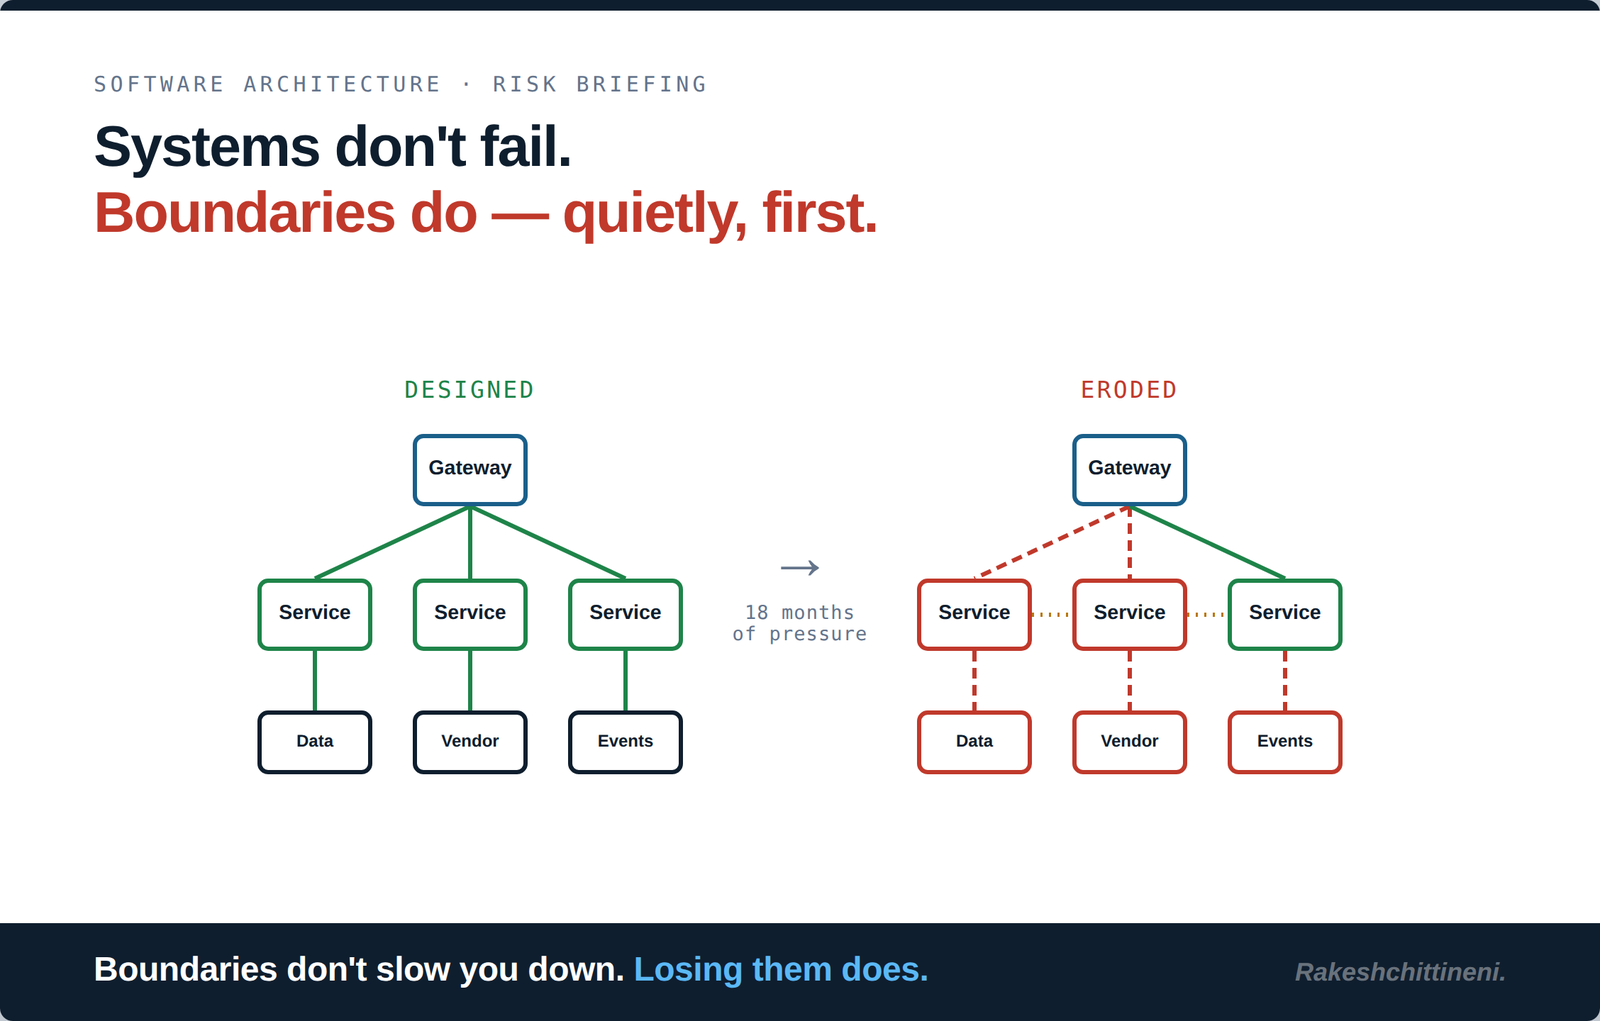
Architecture decides how a production anomaly plays out, not the crisis response plan written afterwards.
Not architecturally ready
- Anomaly in production: no clinical signal detection, only uptime alerts.
- CAPA never starts: no audit trail, and no way to reconstruct what happened.
- Vendor or internal? Unknown. There is no isolation, so investigation takes weeks.
- Recall risk: potentially reportable under 21 CFR 806, with no defensible timeline.
Architecturally ready
- Signal detected immediately: observability built for clinical and security anomalies.
- CAPA triggered with evidence: a full audit trail and a reconstructable event chain.
- Isolated and contained: blast radius boundaries hold, and the SBOM maps the affected component.
- Patch shipped and evidence closed: the update pathway exists by design, with a defensible timeline.
Architecture decides this outcome, not the crisis response plan.
Seen this differently?
Questions, corrections and counterexamples are welcome.