Architecture that holds up in a medical device.
I'm Rakesh Chittineni, a principal software engineer and architect. I write about designing medical device software that stays safe, resilient and explainable under regulatory scrutiny, and where it quietly goes wrong.
Resilient MedTech
Architecture Framework
- The Blast Radius PrincipleClinical operations isolated from corporate IT.
- Designing for the "Dark Day"Safe operation when the cloud is unavailable.
- Intentional ModernizationResilience built in while legacy is modernized.
- Sovereign Systems, Not Silent FleetsHumans keep authority over high-impact decisions.
A reading path through SaMD architecture
New to the site? These six steps take you from where to draw boundaries to how to test your own platform. Each one takes a minute or two.
The framework
Four principles for platforms that keep working when it matters most.
Foundations
How to think before the first box is drawn, and where to draw the lines.
Standards as architecture
Each standard is a design requirement in disguise.
Traceability and the DHF
Evidence is a chain, and gaps hide where standards meet.
Patterns for connected systems
Messaging, modernization and trust, in a regulated setting.
Production and self-check
Post-market readiness is decided at design time. Then test yourself.
Notes from real systems
New writing most weeks. Diagrams you can read in a minute, and longer pieces when a topic needs them.
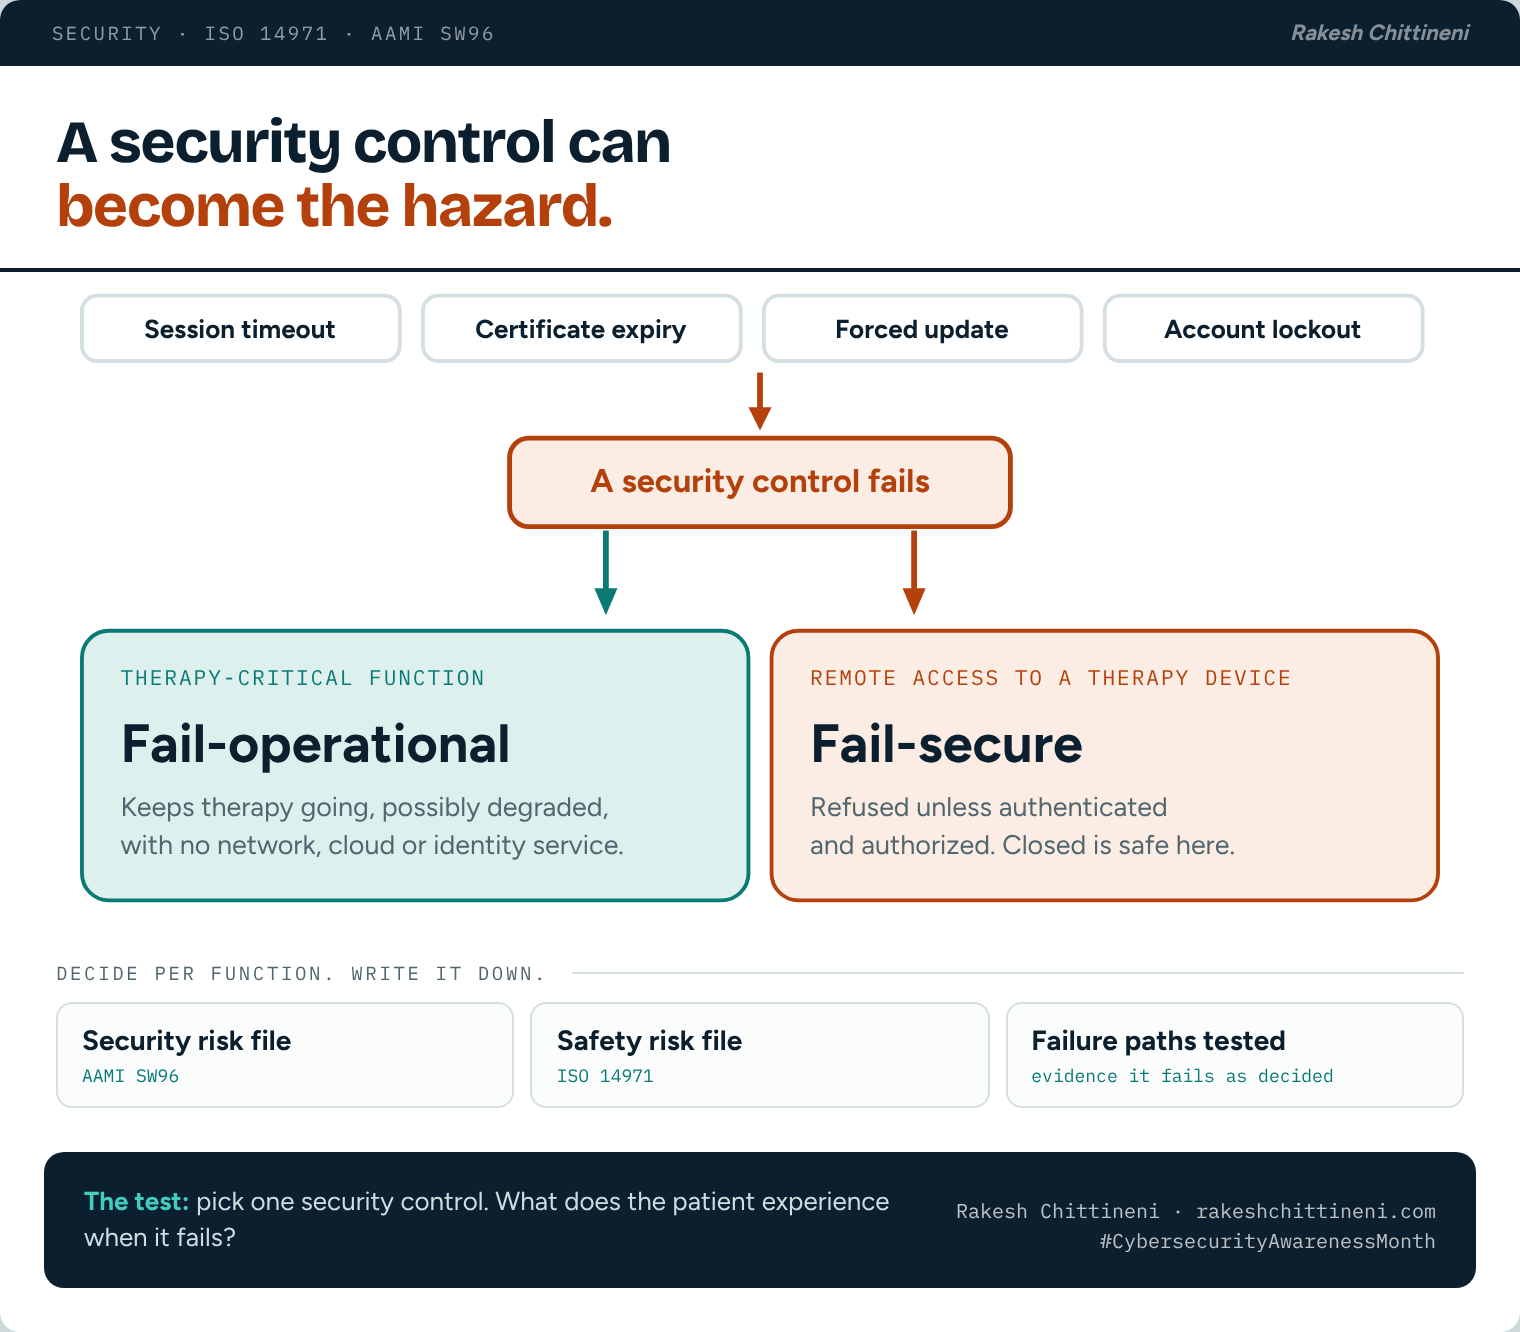
When a security control can hurt the patient
Security controls usually fail closed. In a medical device that default can be the hazard, so whether a function stops, keeps running degraded or refuses access has to be decided per function and written down.
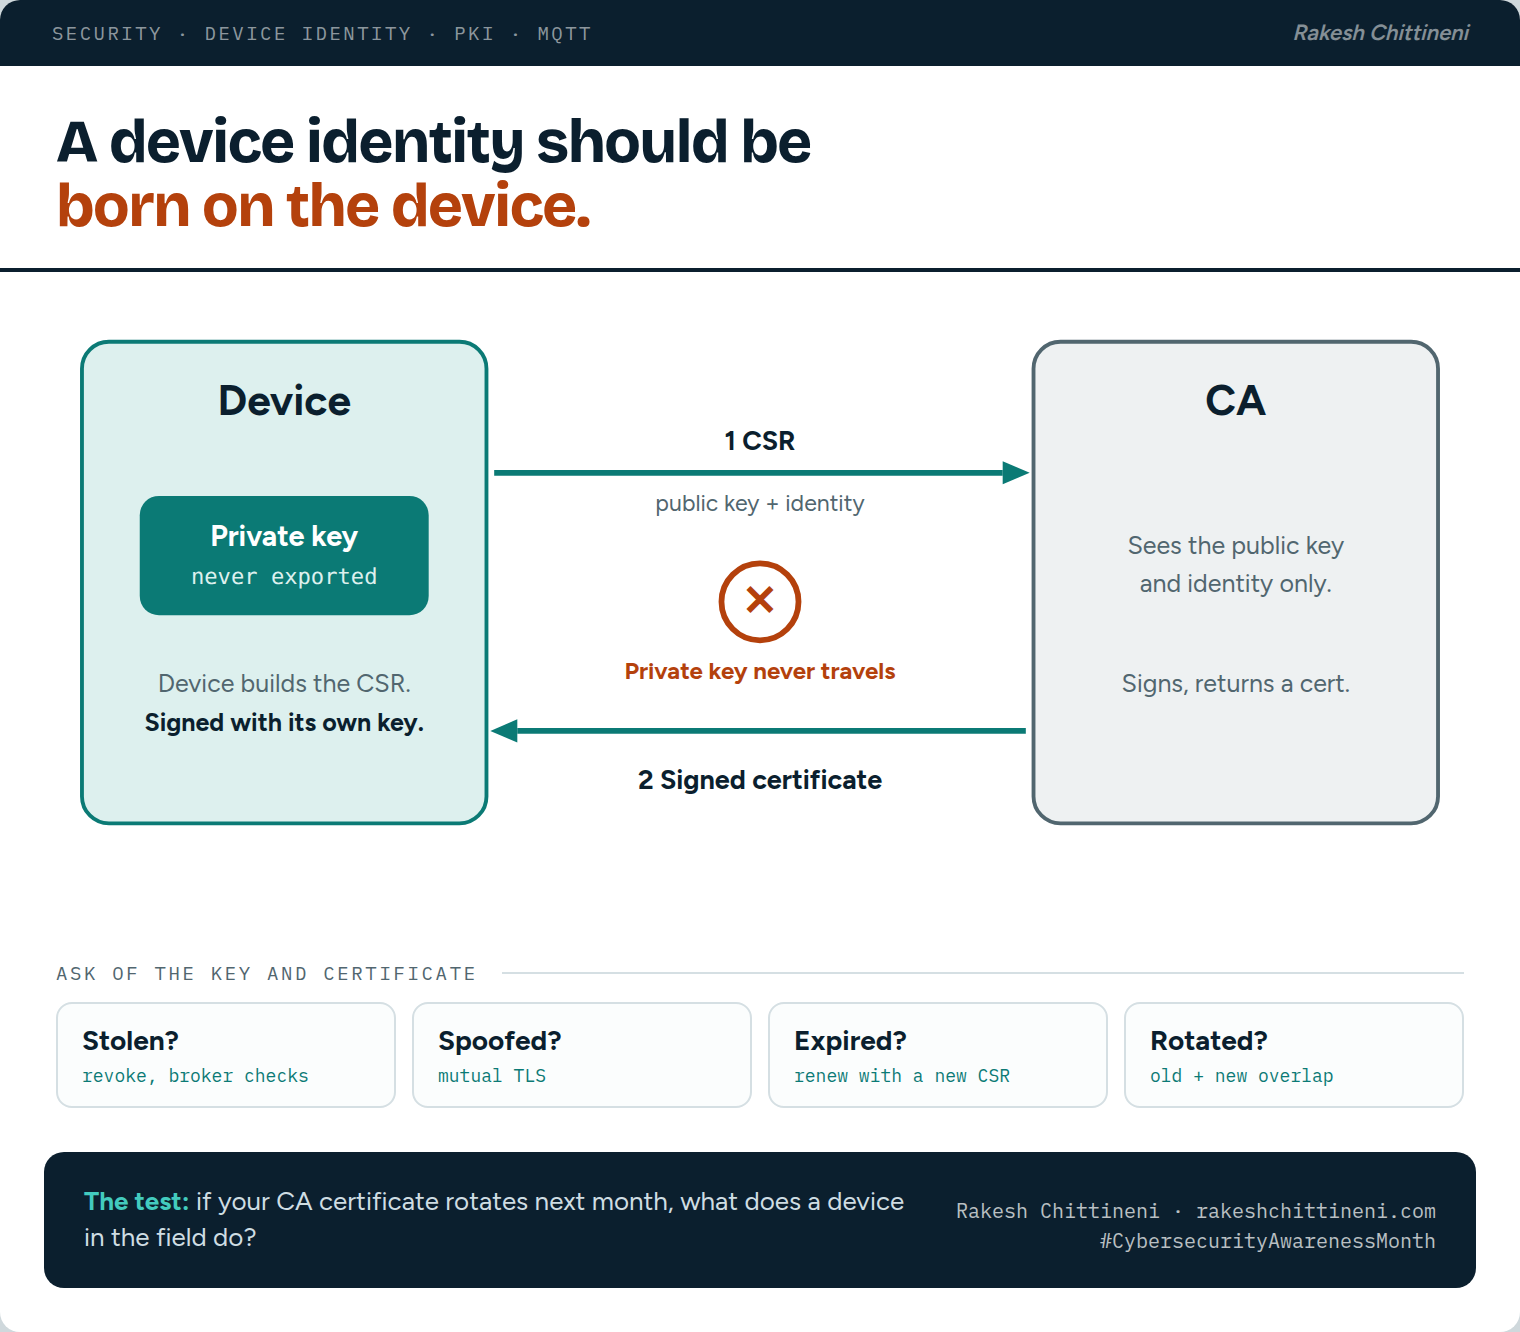
A device identity should be born on the device
Where the private key is created decides how bad a breach can get. Generate it on the device, send only a CSR, and plan for stolen, spoofed, expired and rotated certificates before you ship.
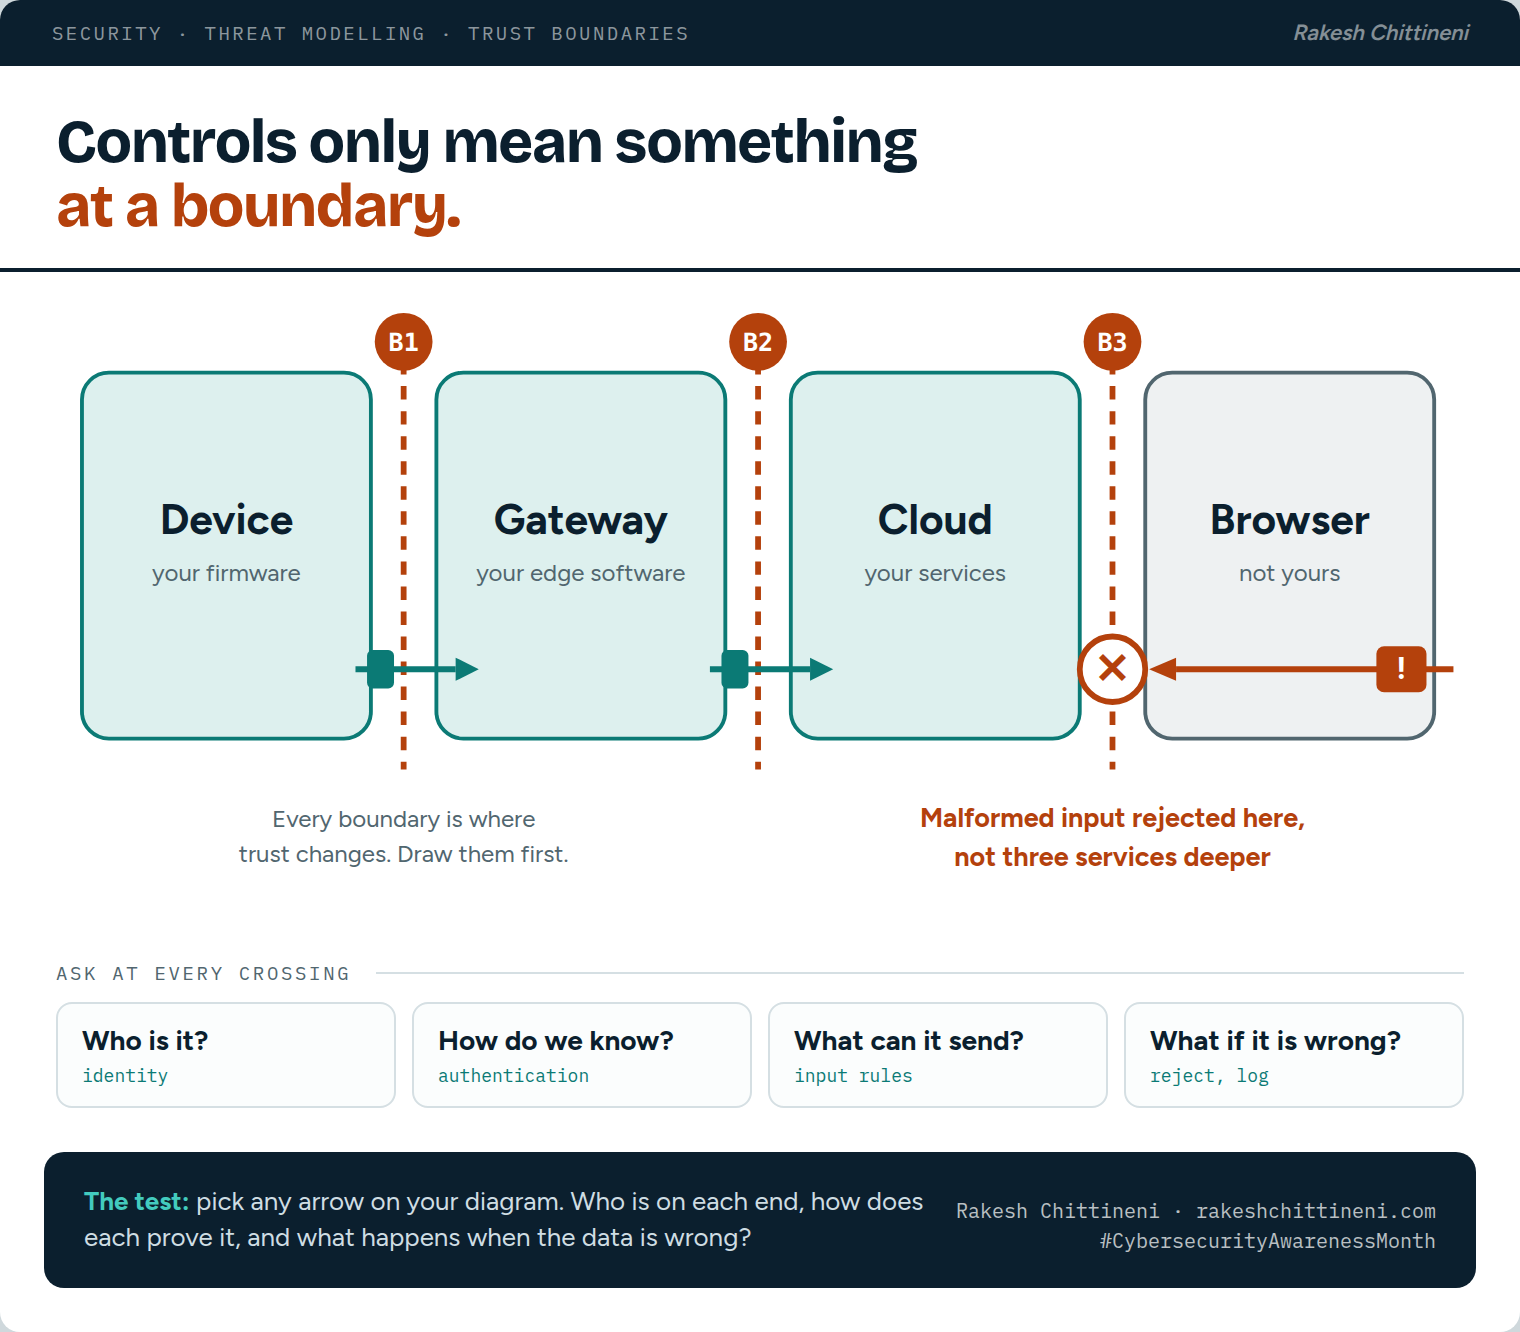
Draw the trust boundaries before you pick the controls
Controls only mean something at a boundary. Map where trust changes first, and the threat model, the requirements and the verification scope follow from it.
Question about something here?
Questions, corrections and counterexamples are welcome. Send a note or message me on LinkedIn.